- Workspace suspension
- Suspending a workspace blocks every user in it from authenticated endpoints.
- Workspace owner and plan changes
- Admins change an owner or a plan and inspect usage and API keys per account.
- User suspension and deletion
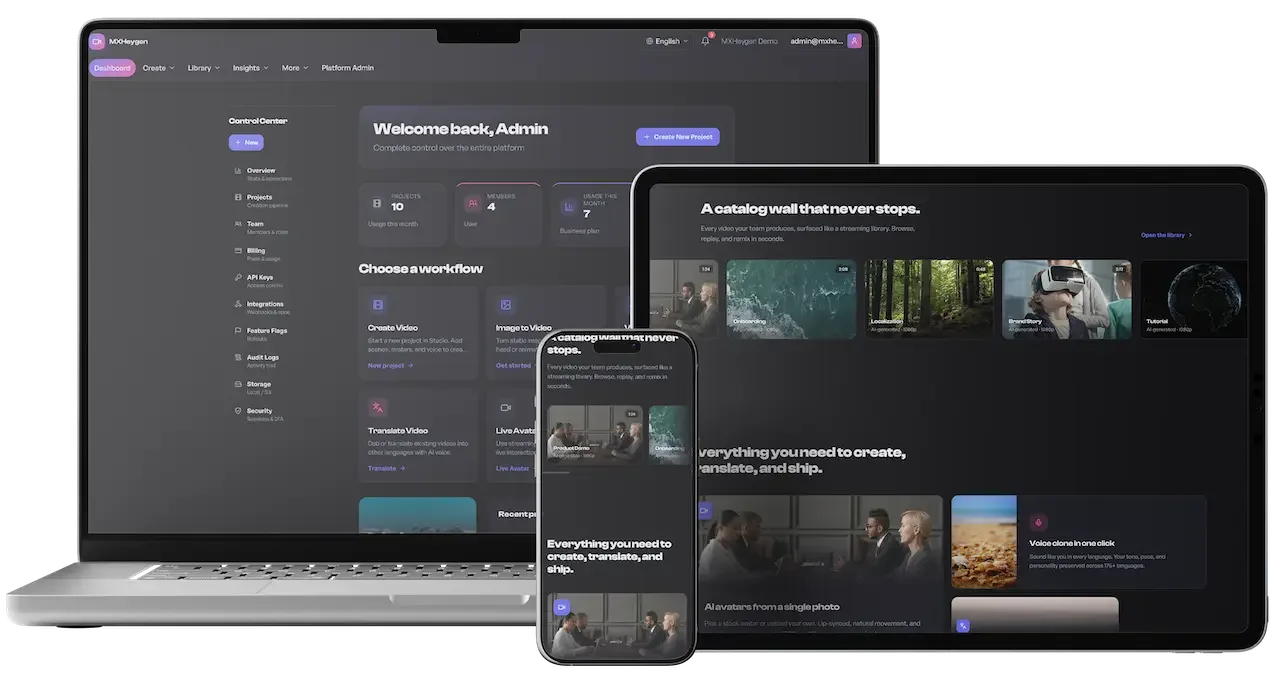
- Accounts can be suspended or deleted from the command center.
- Admin promotion
- Users can be promoted to or demoted from platform admin, controlled by a super-admin flag.
- Support impersonation
- Staff can sign in as a user to reproduce a problem, and impersonation is limited to platform admins.
- Project lifecycle controls
- Projects are archived, restored, deleted or reassigned across workspaces without database access.
- Platform-wide content CRUD
- Avatars, voices, templates, assets and webhooks are managed across the deployment, with scene preview.
- Session control
- Active sessions are listed, and one or all can be revoked for any user.
- Runtime integration config
- Nine integration sections are edited with Save and Test buttons, without a redeploy.
- Runtime settings
- Storage mode, the Redis toggle, feature flags, email, LLM model and billing plans are adjustable at runtime.
- Broadcast messages
- A platform-wide notification reaches every user from one screen.
- Cross-workspace analytics
- Analytics span all workspaces with a period selector, plus oversight of translations and exports.
- Audit log viewer
- A platform-wide trail records the actor, action and resource of security-sensitive events.
- Separate admin authorization
- Every command center route checks the super-admin flag and returns 403 to everyone else.